
TL;DR — KYC/AML at a glance
KYC/AML software is the compliance backbone of any regulated fintech. The honest shape of the build: you integrate vendors for the data- and model-heavy parts and build the decisioning layer regulators hold you accountable for. The essentials:
- Build cost: roughly $180,000–$450,000 for the orchestration, monitoring and case layer on top of integrated vendors.
- You integrate, not invent: identity verification (Persona, Onfido), sanctions/PEP data (ComplyAdvantage), risk signals (Alloy, Sardine) come from specialists.
- You build the decisioning: orchestration, risk rules, the transaction-monitoring engine, case management and SAR reporting.
- Per-check fees are separate — a few dollars per verification and per screen, an operating cost, not build cost.
- Regulation is the frame: US BSA/FinCEN, EU AMLD/6AMLD and the FATF risk-based approach shape every design choice.
- Tuning never stops — keeping false positives manageable is ongoing work, not a launch milestone.
What KYC/AML software actually is
"KYC/AML software" is shorthand for a set of capabilities that, together, let a regulated firm know its customers and detect money laundering. In practice it is six layers:
- Identity verification (IDV) — document checks (passport, ID, proof of address) and biometric liveness/selfie matching at onboarding, confirming a customer is real and who they claim to be.
- Sanctions, PEP & watchlist screening — checking the customer against OFAC, EU, UN and UK sanctions lists, politically-exposed-person databases and adverse media, at onboarding and continuously.
- Transaction monitoring & alerting — rules and models over customer activity that flag suspicious patterns for review.
- Case management — the workbench where analysts investigate alerts, document decisions and escalate.
- SAR & regulatory reporting — filing suspicious-activity reports and periodic regulatory returns in the right format for each jurisdiction.
- Audit trail & data retention — an immutable record of who saw what, who decided what and why, retained for the statutory period.
The first two are mostly bought; the last four are mostly built. See our fintech industry page for how compliance fits the wider fintech stack.
Quick definitions: KYC vs KYB vs AML
The three acronyms get used interchangeably and that causes scoping mistakes. KYC (Know Your Customer) is identity verification and due diligence on an individual. KYB (Know Your Business) is the equivalent check on a company — registration documents, beneficial-ownership chains and the KYC of the humans who own or control it. AML (Anti-Money-Laundering) is the broader compliance programme that KYC/KYB feed into: screening, transaction monitoring, case management and reporting. A marketplace onboarding sellers needs KYB on top of KYC; a consumer app usually needs KYC only. Scope this correctly before pricing a build — adding KYB after launch touches onboarding, the risk-rules engine and reporting at once.
Architecture at a glance
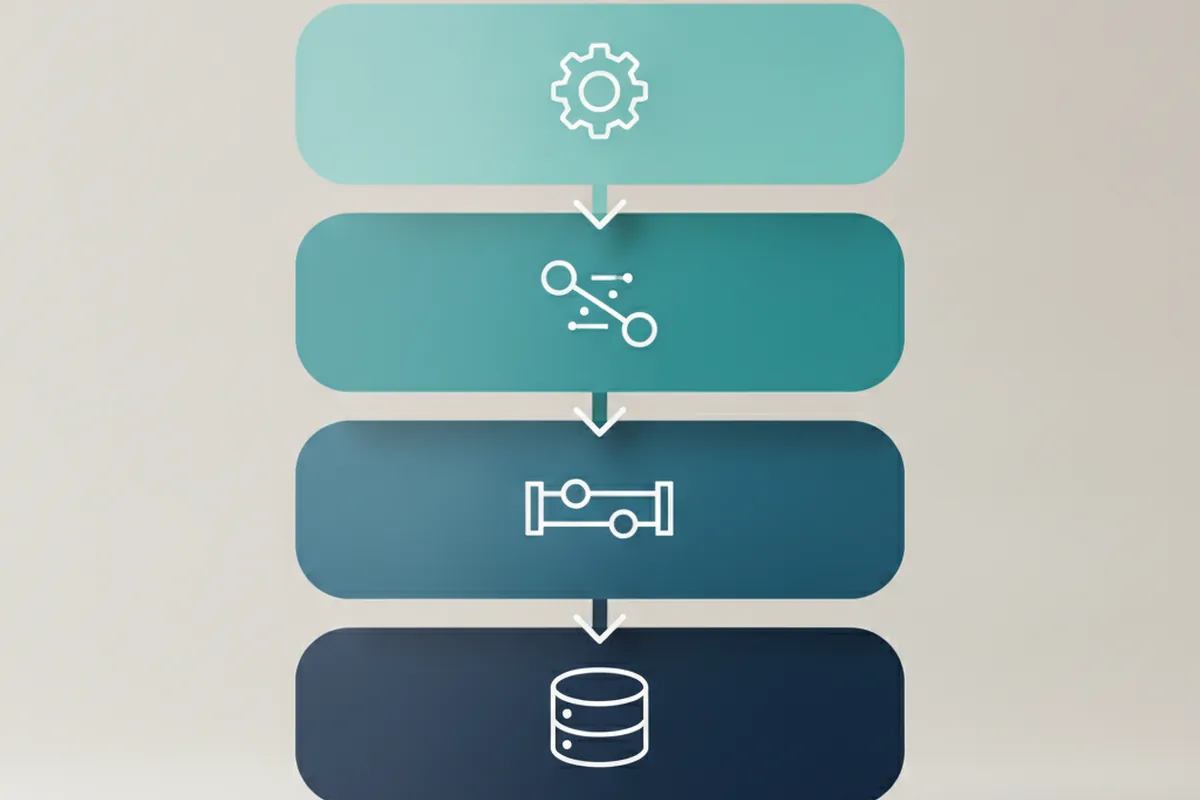
Stripped to its layers, a KYC/AML platform looks the same whether you are a five-person fintech or a bank: an onboarding interface that collects documents and consent; an orchestration and rules-engine layer that sequences IDV, screening and risk checks and applies your scoring logic; a transaction-monitoring pipeline that streams activity through scenarios and produces alerts; and a secure, append-only audit-log and data-retention layer underneath everything, because every decision has to be reconstructable years later for an examiner. Vendors plug into the middle two layers as data and model providers; your team owns the orchestration logic, the queue that routes alerts to analysts, and the audit trail.
Build vs integrate a vendor
This is the decision that sets the cost. It is also where a lot of misleading proposals live. Here is the honest framing.
You integrate specialist vendors for the parts that are data-heavy, model-heavy and constantly changing. Identity verification (Persona, Onfido) is a deep biometric and document-forensics problem. Sanctions and PEP data (ComplyAdvantage) is a curated dataset that changes every day. Fraud and risk signals come from firms whose whole business is keeping those models current: Alloy for orchestration and decisioning, Sardine for behavioural and fraud signals. None of this is worth rebuilding yourself.
You build the orchestration and decisioning layer. This is the part that is specific to your firm, and the part regulators hold you accountable for. It covers the flow that sequences IDV, screening and risk checks during onboarding. It also covers your own risk-scoring rules, the transaction-monitoring engine and its scenarios, the case-management queue your analysts work in, your SAR and reporting workflow, and the audit trail.
| Component | Integrate (buy) | Build (own) |
|---|---|---|
| Identity verification & biometrics | ✅ vendor API | Onboarding flow around it |
| Sanctions / PEP / adverse-media data | ✅ data subscription | Matching tolerance, alert queue |
| Risk-scoring rules & thresholds | — | ✅ yours, encodes risk appetite |
| Transaction-monitoring engine | Signals only (e.g. Sardine) | ✅ scenarios, scoring, tuning |
| Case management & SAR workflow | — | ✅ almost always in-house |
| Audit trail & data retention | Infra only (cloud/DB) | ✅ schema, access control, retention policy |
Vendor landscape — who you integrate
Because the data- and model-heavy layers are bought, choosing vendors is an early, cost-shaping decision. The table below lists representative players by layer as of 2026. Treat it as a shortlist to price and pilot, not an endorsement. Availability, coverage and pricing vary by market, so verify against your jurisdictions before committing.
| Layer | Representative vendors (2026) | What you are buying |
|---|---|---|
| Identity verification (IDV) | Persona, Onfido, Veriff, Jumio | Document forensics + biometric liveness/selfie matching |
| Sanctions, PEP & adverse media | ComplyAdvantage, Dow Jones, LSEG World-Check | Curated, daily-updated screening datasets |
| Onboarding orchestration & fraud | Alloy, Sardine | Decisioning orchestration + behavioural fraud signals |
| On-chain analytics (crypto) | Chainalysis, Elliptic, TRM Labs | Wallet screening + blockchain risk scoring |
| Travel Rule messaging (crypto) | Notabene, Sygna, TRP protocol | Originator/beneficiary data exchange between VASPs |
Note the pattern: every row is data or a maintained model, never decisioning logic. You subscribe to these, then build the orchestration, rules and case layer that sequences and acts on them. That case layer is exactly what the cost breakdown below prices.
Step-by-step: how a KYC/AML build actually runs
Skip the generic "discovery, design, build, launch" template — here is what each phase actually involves for a compliance product, in the order that avoids rework.
- Compliance and risk mapping. Before any code, define which jurisdictions, products and customer types you serve, and what due-diligence depth each requires. This determines which vendors you can even shortlist, so it has to happen first, ideally with compliance counsel in the room.
- Vendor selection and contracting. Shortlist and pilot IDV, screening and risk-signal vendors against real test cases from your target markets. Start contracting immediately — procurement and security review at a vendor can take weeks and this is the most common source of schedule slip.
- Architecture and data-model design. Design the orchestration flow, the case and audit data model, and the retention and access-control policy before writing the monitoring engine — retrofitting audit requirements onto an existing schema is expensive.
- Core development. Build in parallel: onboarding orchestration and IDV/screening integration on one track, the transaction-monitoring rules engine and case-management workbench on another. This is where most of the $180k–$450k build budget goes (see the breakdown below).
- Testing and validation. Beyond functional QA, this means testing the monitoring rules against historical or synthetic transaction data to check false-positive and false-negative rates, and a dry run of the SAR filing workflow end to end.
- Launch, monitor and tune. Go live with conservative thresholds, watch alert volume and analyst throughput closely in the first weeks, and tune the rules engine. Treat this as ongoing operations, not a post-launch cleanup task.
Cost breakdown by module
Indicative build costs for a fintech assembling KYC/AML capability on top of integrated vendors. Ongoing per-check vendor fees are not included — they are a separate operating cost.
| Module | Build cost | Notes |
|---|---|---|
| IDV / onboarding integration | $35k–$70k | Vendor (Persona/Onfido) integration + onboarding flows |
| Sanctions + PEP screening | $30k–$60k | Data provider integration, matching, alert queue |
| Transaction monitoring engine | $50k–$110k | Rules/scenarios, scoring, alerting; tuning ongoing |
| Case management & SAR reporting | $40k–$90k | Investigator workbench, four-eyes review, filings |
| Audit trail & data retention | $25k–$55k | Immutable logs, retention, access controls |
| Ongoing per-check vendor fees | Separate (operating cost) | ~$1–$5 per IDV; per-screen/monitoring fees |
That lands the build in the $180,000–$450,000 range. For where this sits in a wider product budget, see our neobank development cost breakdown; for moving money around it, our payment gateway integration guide.
Regulatory backdrop
KYC/AML software exists to satisfy specific legal obligations, and the enforcement is real money: global penalties for AML, KYC and sanctions failures totalled $3.8 billion in 2025, down from $4.6 billion in 2024, according to Fenergo's Global AML Fines Research — with enforcement shifting from the US toward EMEA and APAC. The major frameworks, as general guidance:
- US — BSA / FinCEN: the Bank Secrecy Act and FinCEN rules require a Customer Identification Program (CIP), customer due diligence, ongoing monitoring and the filing of Suspicious Activity Reports (SARs) and Currency Transaction Reports.
- EU — AMLD / 6AMLD: the Anti-Money-Laundering Directives set customer due-diligence, screening, beneficial-ownership and reporting obligations, now consolidating under a new single EU rulebook and AML authority (AMLA).
- FATF risk-based approach: the through-line of both regimes — you calibrate the depth of due diligence to the risk a customer or transaction presents, applying enhanced due diligence to higher-risk cases.
- Crypto & the Travel Rule: virtual-asset firms must, under the FATF Travel Rule, pass originator and beneficiary information alongside transfers above thresholds, on top of standard KYC/AML.
This is general guidance, not legal advice. Your exact obligations depend on your licences, products and jurisdictions. Engage qualified compliance counsel, and build the software to match the policy they help you set.
Transaction monitoring and case management
These two modules absorb the most budget and the most ongoing effort, so they deserve detail.
The monitoring engine
Transaction monitoring runs scenarios over activity and raises alerts. The scenarios look for structuring, velocity spikes, unusual counterparties, or behaviour that does not fit the customer's stated profile. Start with a transparent, explainable rules engine: regulators expect you to justify every alert and every cleared case, and a black-box model you cannot explain is a liability. Layer machine-learning scoring on later, once you have data and a baseline, to cut the false-positive rate. And tune the thresholds continuously. An untuned engine either drowns analysts in noise or, worse, misses real risk.
Case management and reporting
Every alert, whether from screening or monitoring, lands in a case queue with the relevant customer and transaction context attached. Analysts investigate, document their reasoning, apply four-eyes review where required, and either clear the alert or escalate it to a SAR. This workbench is the part of the stack that most clearly embodies your firm's risk policy. It is also the first thing an examiner asks to see, which is why teams almost always build it rather than buy it.
Common implementation challenges (and how to avoid them)
Most KYC/AML builds run into the same handful of problems. Knowing them upfront is cheaper than discovering them after launch.
- Alert fatigue from an untuned rules engine. Ship with thresholds too tight and analysts drown in false positives, which trains them to click through alerts without reading them — the exact failure mode examiners look for. Start conservative, measure the false-positive rate weekly, and tune deliberately.
- Vendor lock-in through the orchestration layer. If your screening or IDV vendor's SDK is woven directly through your onboarding code, switching providers later means a rebuild, not a swap. Keep vendor calls behind your own orchestration interface from day one.
- Cross-border rule divergence. A US-only rules engine breaks the first time you onboard an EU customer under 6AMLD due-diligence rules, or vice versa. Model jurisdiction-specific due-diligence depth and reporting format as configuration on one platform, not as a fork.
- Explainability gaps in ML scoring. A black-box risk model that flags a customer but cannot say why is a liability in front of a regulator. Launch with an explainable rules engine and only add ML scoring once you can justify every score component.
- Underestimating the audit trail. Teams often treat logging as an afterthought, then discover during an exam that they cannot reconstruct who reviewed a specific alert eighteen months ago. Design retention and access-control requirements into the schema before the monitoring engine, not after.
- Compliance and engineering working in silos. Rules that make sense to a compliance officer on a whiteboard often do not translate cleanly into code, and vice versa. Keep a compliance SME embedded through the core-development phase, not just at sign-off.
Timeline, team and phasing
A first production-grade KYC/AML capability typically takes 4–7 months. Vendor selection, contracting and sandbox-then-production API integration for IDV and screening often sit on the critical path, so start them in week one. A typical team looks like this: a product- and compliance-aware delivery lead, two backend engineers (one focused on the monitoring engine and data model), a frontend engineer for the case-management workbench, QA with a security mindset, and part-time DevOps plus a compliance SME or external advisor.
Phase it: onboarding IDV + screening + a baseline rules engine + case management + basic reporting first; defer ML scoring, adverse-media depth, on-chain analytics and advanced reporting to later. Many fintechs assemble the team through a dedicated development team to control cost while keeping the compliance-critical logic in-house.
How to control the cost
- Buy the data and models — never rebuild IDV, sanctions data or watchlists.
- Build the decisioning layer — orchestration, rules, case management and audit are yours and are non-negotiable.
- Start with explainable rules — defer ML scoring until you have data; regulators want explainability first.
- Start vendor onboarding in week one — contracting and API access are usually the critical path.
- Treat market rules as configuration — one platform, configured per jurisdiction, beats two separate builds.
- Choose a partner who has shipped regulated fintech before — the case and audit layer is where inexperience gets expensive.
This is core custom software work, with card and payment paths often built to PCI-DSS scope; the right team and a phased plan are the main cost levers.
FAQ
What is KYC/AML software?
KYC/AML software is the compliance backbone of a regulated fintech. It covers onboarding identity verification (IDV) — document and biometric checks that confirm a customer is who they claim to be — plus sanctions, PEP and watchlist screening, ongoing transaction monitoring and alerting, case management for investigators, suspicious-activity (SAR) and regulatory reporting, and an immutable audit trail. Together these let a firm meet its Know-Your-Customer and Anti-Money-Laundering obligations. In practice you integrate specialist vendors for IDV and screening data, and build the orchestration, risk-rules and case-management layer that ties them together.
Should I build KYC/AML software or buy a vendor?
Both — and the split matters. You integrate vendors for the parts that are data- or model-heavy and constantly changing: identity verification (Persona, Onfido), sanctions and PEP data (ComplyAdvantage), and fraud/risk signals (Alloy, Sardine). You build the orchestration layer that sequences those checks, your own risk-scoring rules, the case-management queue your analysts work in, your SAR and reporting workflow, and the audit trail. Nobody sane builds their own sanctions watchlists or rebuilds biometric IDV from scratch. The differentiator and the part regulators hold you accountable for is the decisioning and case layer — that is what you build.
How much does it cost to build KYC/AML software?
For a fintech building the orchestration and case-management layer on top of integrated vendors, expect roughly $180,000–$450,000 in build cost. That spans IDV/onboarding integration ($35k–$70k), sanctions and PEP screening integration ($30k–$60k), a transaction-monitoring engine ($50k–$110k), case management and SAR reporting ($40k–$90k), and audit and data-retention infrastructure ($25k–$55k). On top of the build sit ongoing per-check vendor fees — typically a few dollars per identity verification and per ongoing screening — which are separate operating costs, not build cost, and need to be modelled into your unit economics.
How does AML transaction monitoring work?
Transaction monitoring runs rules and models over customer activity to flag patterns that may indicate money laundering — structuring, rapid movement, unusual counterparties, velocity spikes, or behaviour inconsistent with the customer's stated profile. Flagged activity becomes an alert in the case-management queue, where an analyst investigates and decides whether to file a suspicious-activity report. Most fintechs start with a transparent, explainable rules engine (thresholds and scenarios) because regulators expect you to justify every alert, and layer in machine-learning scoring later to cut false positives. The monitoring engine and its rules are something you build and tune; it is rarely a pure off-the-shelf component.
What regulations govern KYC/AML software?
In the US, the Bank Secrecy Act (BSA) and FinCEN rules require a Customer Identification Program, ongoing monitoring and suspicious-activity reporting. In the EU, the Anti-Money-Laundering Directives (the 6th, 6AMLD, being the most recent) set customer due-diligence, screening and reporting obligations, now consolidating under a new EU AML authority and rulebook. The FATF risk-based approach underpins both: you calibrate the depth of due diligence to the risk a customer or transaction presents. Crypto firms additionally face the FATF Travel Rule, which requires originator and beneficiary information to travel with transfers. This is general guidance, not legal advice — your specific obligations depend on your licences, products and jurisdictions, so engage qualified compliance counsel.
What is case management in AML software?
Case management is the workbench where compliance analysts handle alerts. When screening or transaction monitoring raises a flag, it lands in a queue as a case with the relevant customer data, transaction history and prior decisions attached. The analyst investigates, documents their reasoning, and either clears the alert or escalates it to a suspicious-activity report. Good case management gives an audit trail of who decided what and why, supports four-eyes review, and feeds reporting. It is the part of the stack you almost always build yourself, because it embodies your firm's specific risk policy and is exactly what an examiner or auditor will scrutinise.
What is the difference between KYC, KYB and AML?
KYC (Know Your Customer) verifies an individual's identity. KYB (Know Your Business) does the equivalent for a company — registration documents, ownership structure and the KYC of the humans behind it. AML (Anti-Money-Laundering) is the umbrella programme that both feed into: screening, transaction monitoring, case management and reporting. A platform onboarding both consumers and businesses needs KYC and KYB; get the scope wrong at design time and adding the missing one later touches onboarding, risk rules and reporting all at once.
What are the most common mistakes in a KYC/AML build?
The recurring ones: shipping monitoring thresholds so tight that analysts drown in false positives and start clicking through alerts without reading them; wiring a vendor's SDK directly into onboarding code instead of behind your own orchestration layer, which creates lock-in; treating cross-border rule differences as a fork instead of configuration; deploying an ML risk model you cannot explain to an examiner; and treating the audit trail as an afterthought instead of designing its retention and access rules before the monitoring engine.
Last updated 26 September 2026. Cost ranges reflect vendor-integrated agency builds for US and EU markets and vary by scope, products, market and vendor mix. Regulatory references (BSA/FinCEN, EU AMLD/6AMLD, FATF) are general guidance, not legal advice — consult qualified counsel for your jurisdiction. Request a scoped proposal for your specific KYC/AML programme.