
The short answer
Cisco Talos disclosed CLOSEDQUORUM, a Windows implant that asks a panel of four commercial large language models — DeepSeek, Qwen, Mistral, and Google Gemini — to vote on its next action instead of waiting for a human operator or a fixed C2 server. The 16.4MB Go binary was surfaced with CAIRN, an open-source toolkit Talos released the same day to hunt AI-integrated malware. The single most important caveat: Talos has not confirmed the malware in the wild, the public sample does not run end to end, and there is no victim count. This is a capability signal, not an outbreak — a working demonstration that autonomous, LLM-driven agent logic is now being wired into offensive tooling.
The lesson for defenders is not “a new virus is spreading.” It is that outbound calls to AI model providers are now a security-relevant behavior on your endpoints and servers. When an implant’s decision logic lives in prompts and votes rather than in a hard-coded address, static signatures weaken and detection has to move to behavior.
What Talos found — and why it matters
Cisco Talos published its findings on Tuesday, September 22, 2026, opening a new research series with CLOSEDQUORUM and releasing CAIRN — the Cognitive Artifact Intelligence Research Network — an open-source toolkit to hunt, classify, and track malware that leans on large language models. In Talos’ own framing, CLOSEDQUORUM is the first publicly documented Windows implant to apply an LLM-panel model to tactical command and control: it “delegates the selection of its next action to a panel of commercial large language models and executes the resulting decision” without continued commands from a human operator or tasking from a dedicated, attacker-operated C2 server.
The honest headline is a capability, not a crisis. Talos was careful to say it does not have confirmation of in-the-wild deployment, is not reporting a mass-infection event, a confirmed victim count, or a prevalence figure, and that the public version of the binary does not function as-is. What it did find is a 16.4MB Go binary whose developer artifacts connect to postings on criminal forums related to carding dating back to 2025. In other words: someone is building this, and shopping the surrounding trade, even if this particular sample is not a finished weapon.
Why does an unfinished proof-of-concept matter to teams that build and run software? Because it collapses a barrier. Traditional command-and-control needs infrastructure an attacker has to stand up, hide, and keep online — and that infrastructure is exactly what defenders and takedowns target. An implant that instead reaches out to mainstream model APIs for its decisions blends into traffic that many networks now consider normal, and it keeps operating even when no operator is watching. That is a structural shift worth threat-modeling before it is a widespread one.
How a “quorum” of LLMs runs the attack
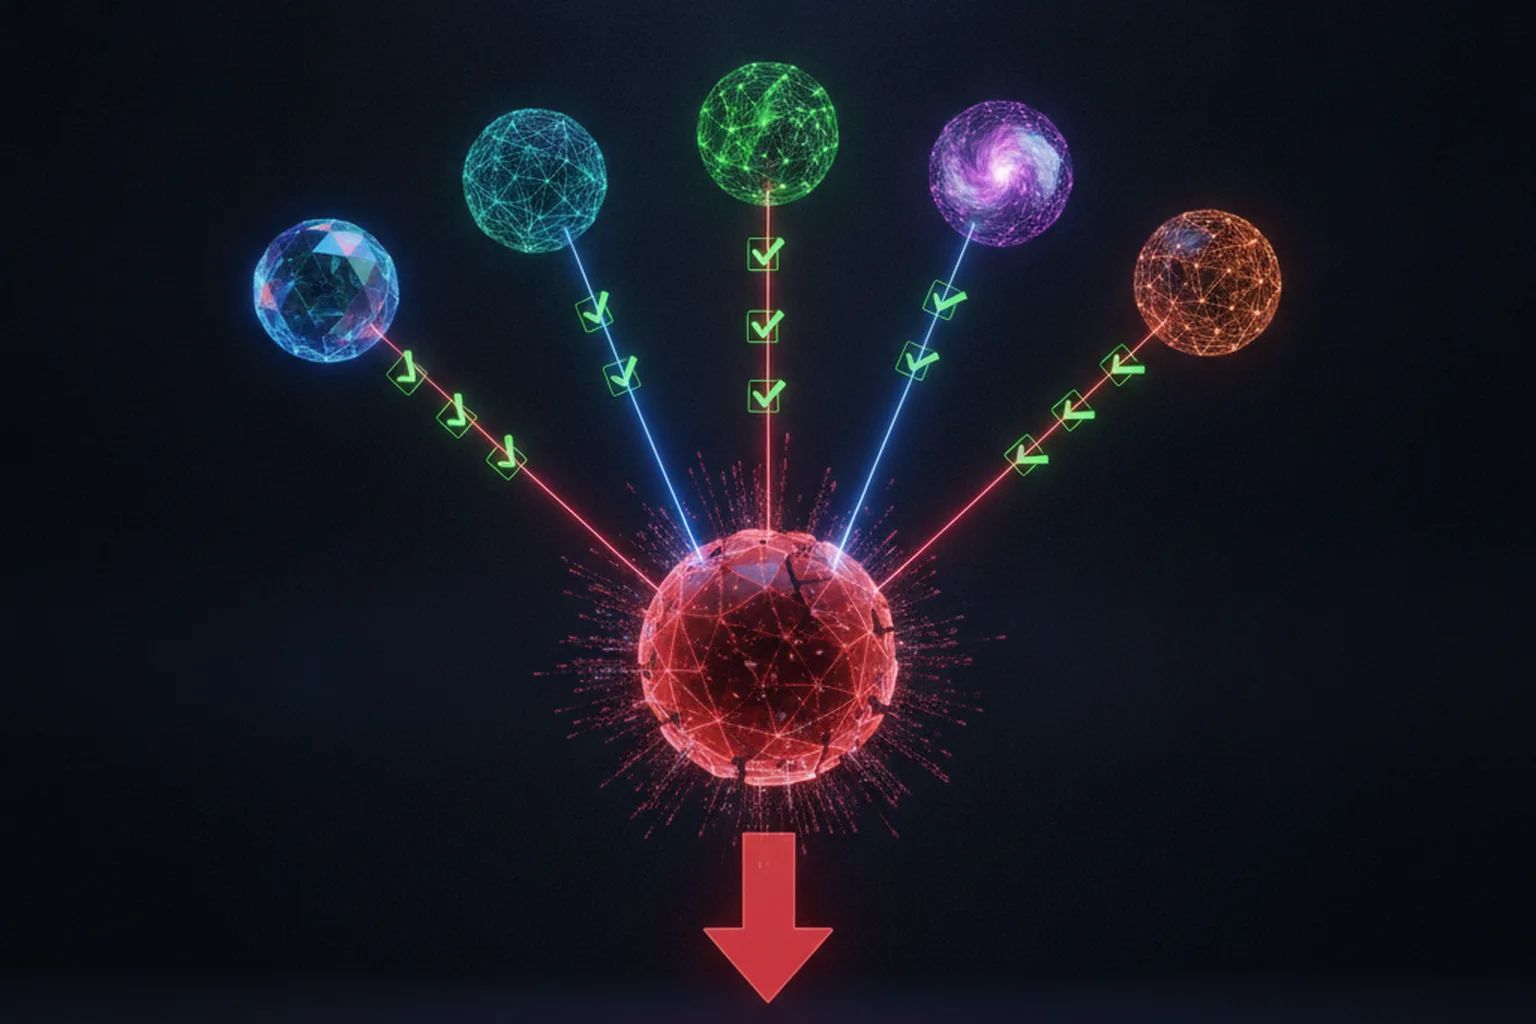
The name is the mechanism. CLOSEDQUORUM convenes an internal quorum of four commercial models — DeepSeek, Qwen, Mistral, and Google Gemini — and puts a decision to them: given the current state of the compromised host, what should the malware do next? Each model returns a choice from a fixed menu of actions, the implant tallies a plurality vote, and it executes whichever action wins. Talos’ reporting describes that menu as a small, bounded set: steal (credentials, saved browser passwords, crypto-wallet data), inject into a process, establish persistence, and move laterally.
Two design choices are worth pulling out. First, the action set is constrained. The models are not writing arbitrary code on the fly; they are selecting from options the author defined, which makes the behavior more reliable and, notably, easier to reason about than free-form AI code generation. Second, using several models and voting is a hedge: it smooths over any single provider refusing a request, going offline, or returning a bad answer, and it avoids a single hard dependency that a defender could cut. If operated as assessed, Talos says, the result resembles a credentials-as-a-service model whose real differentiator is that autonomous orchestration layer — an operator drops the binary and the panel runs the attack without the operator needing to stay online.
It is also why signatures struggle. There is no fixed C2 domain to block and no static command string to match, because the “instructions” are generated per-run by third-party models. Talos’ guidance is therefore behavioral: the tell is a single unknown binary that contacts several commercial LLM endpoints while simultaneously doing suspicious local things — reading LSASS memory, injecting into suspended processes, or creating WMI persistence. That combination — model chatter plus hands-on-keyboard techniques from one process — is the anomaly, and it is the kind of pattern CAIRN is built to surface.
What it means for US & EU software teams
The first shift is that LLM API traffic is now part of your attack surface. For most engineering orgs, calls to OpenAI, Google, Mistral, and others have quietly become routine — from copilots, agents, and internal tools — which is precisely why a malicious process can hide inside them. That means inventorying which hosts and services legitimately talk to model providers, and tightening egress so that a random workstation or server reaching four LLM APIs at once is an event, not background noise. This is standard cloud and DevOps hardening applied to a new signal.
The second shift is for teams shipping their own AI features. CLOSEDQUORUM is offensive tooling, but its architecture is a mirror of the agent patterns many products are adopting: give a model a goal, a set of tools, and let it decide. The defensive takeaways transfer directly to building AI and data systems responsibly — constrain the action set an agent can take, require human approval for high-impact steps, log every decision the model makes, and assume the model layer can be probed or manipulated. An agent you build with a bounded, audited toolset is both safer and easier to defend than one with open-ended capabilities.
The third shift is about proportion. This is not the moment to panic-buy or to treat every LLM call as hostile; Talos itself declined to inflate the finding. It is the moment to update threat models and detections so that when a finished, in-the-wild version of this pattern does appear — and the incentives suggest one will — your team already knows what “a process that phones a committee of models” looks like on the wire and on the host.
What to do now
- Inventory your LLM egress. Know which hosts, services, and users legitimately reach commercial model APIs. You cannot flag anomalous AI traffic until you know what normal looks like.
- Tighten outbound controls. Restrict model-provider endpoints to sanctioned services and hosts. A general-purpose workstation or backend suddenly contacting multiple LLM APIs should generate an alert.
- Detect on behavior, not addresses. Hunt for one process combining LLM API calls with LSASS access, injection into suspended processes, or WMI persistence. Evaluate open-source tooling like CAIRN for this class of threat.
- Harden the endpoints CLOSEDQUORUM targets. Credential theft, process injection, and persistence are the actual actions on the menu — so credential-guard protections, EDR on injection, and persistence monitoring still do the heavy lifting.
- Constrain your own agents. If you build with autonomous LLM agents, bound their tools, require approval for high-impact actions, and log decisions — the same controls that make an agent trustworthy make it defensible.
Frequently asked questions
What is CLOSEDQUORUM and when was it disclosed?
CLOSEDQUORUM is a Windows implant that Cisco Talos disclosed on September 22, 2026, describing it as the first publicly documented malware to delegate tactical command-and-control decisions to a panel of commercial large language models. Instead of waiting for commands from a human operator or a dedicated attacker-run server, the binary asks a group of LLMs to vote on its next action and then executes the winner. Talos found it using CAIRN, an open-source toolkit it released the same day for hunting AI-integrated malware.
Which AI models does CLOSEDQUORUM use, and how do they decide?
The implant convenes a panel of four commercial large language models — DeepSeek, Qwen, Mistral, and Google Gemini — and lets them choose the next step from a fixed set of actions such as stealing credentials, injecting into a process, establishing persistence, and moving laterally. The action that wins the plurality vote is the one the malware runs. That autonomous LLM orchestration layer, not hard-coded control flow or live operator tasking, is the differentiator Talos highlights.
Has CLOSEDQUORUM been seen infecting real organizations?
No. Talos was explicit that it does not have confirmation of in-the-wild deployment, is not reporting a mass-infection event or a confirmed victim count, and that the public version of the binary does not run end to end as-is. The finding matters as a design and capability signal — a proof that autonomous LLM-driven C2 is now buildable and appearing on criminal forums — rather than as an active outbreak. Talos linked developer artifacts to forum postings related to carding dating back to 2025.
How can defenders detect malware that uses LLMs for command and control?
Because the malicious logic lives in prompts and votes rather than in a fixed C2 address, static signatures are weak. Talos recommends behavioral detection: watch for a single unknown binary that contacts several commercial LLM API endpoints while also performing suspicious local actions such as reading LSASS memory, injecting into suspended processes, or creating WMI persistence. Talos released CAIRN as an open-source toolkit to hunt, classify, and track this class of AI-integrated malware.
What does CLOSEDQUORUM mean for US and EU software teams?
It reframes outbound calls to LLM providers as a security-relevant event on endpoints and servers, not just a productivity feature. Teams should inventory and monitor model-provider API traffic, tighten egress so only sanctioned services and hosts can reach those endpoints, and add the behavior to their threat models. For teams building autonomous AI agents, it is also a reminder to constrain what an agent can do, log its decisions, and keep a human approval step on high-impact actions.
Sources
Cisco Talos — The Closed Quorum: Inside the first reported autonomous AI C2 implant (primary research)
The Hacker News — This Windows Malware Is Built to Let Up to Four AI Models Vote on Its Next Move