
API software development sits behind almost every digital product you use. When a mobile app shows your order status, when a checkout charges a card, when a CRM pulls leads from a website form or when an AI assistant books a meeting, one piece of software is asking another for data or an action through an API. If those interfaces are badly designed, every new feature, partner and app becomes slower and riskier to ship.
For most companies, APIs are not a separate project but the backbone of their product. That is why we treat API and backend development for custom web applications as one discipline: the same contract serves the web app, the mobile app, partners and internal tools. Getting that contract right early is far cheaper than rewriting it after clients depend on it.
This guide explains what an API is in software development, how APIs work, the main types and protocols, how a professional API development process runs, which tools are standard in 2026, how to secure an API, what it costs and how to choose a team. It is written for founders, product owners and engineering leads who need to make decisions, not memorize specifications.
What is API software development?
API software development is the work of designing, building, testing, securing, documenting and operating application programming interfaces. An API is a contract: it states which requests a system accepts, what data must be sent, what comes back and what errors can happen. Developers on the other side can rely on that contract without seeing the code behind it.
A complete API project covers more than writing endpoints. It includes interface design, the business logic and data access behind each operation, authentication and authorization, input validation, rate limiting, versioning, documentation, automated tests, deployment and monitoring. Skipping any of these usually shows up later as broken integrations, security incidents or support tickets from partners.
What does API mean in software development?
In software development, API stands for application programming interface: a defined way for one program to talk to another. The word “interface” is the key. Just as a power socket hides the power plant behind a standard plug shape, an API hides a system’s internal code, database and infrastructure behind a stable set of requests and responses.
The API definition in software development has three parts: what you can ask for (operations or endpoints), how you must ask (protocol, format, authentication) and what you get back (data and status codes). If both sides follow that definition, they can be written in different languages, run on different clouds and be updated independently.
Basic API terminology
A handful of terms appear in every API conversation. Knowing them makes vendor proposals and technical documentation much easier to read.
| Term | What it means | Example |
|---|---|---|
| Endpoint | An address where the API accepts a specific type of request | /orders/{id} |
| Request | A message from the client asking for data or an action | GET order 1042 |
| Response | The server’s reply with data and a status code | JSON with order details, 200 OK |
| HTTP method | The type of action in REST APIs | GET, POST, PUT, PATCH, DELETE |
| Status code | A number that tells the client whether the call worked | 200 success, 404 not found, 429 too many requests |
| Schema / contract | A machine-readable description of all endpoints and data | OpenAPI file, GraphQL schema, Protobuf file |
| Authentication | Proof of who is calling the API | OAuth 2.0 token, API key, mTLS certificate |
| Rate limit | A cap on how many calls a client can make in a period | 100 requests per minute per key |
How does an API work?
An API works through a request-response cycle: a client sends a structured request to an endpoint, the server checks who is calling and whether the request is valid, runs the business logic, and returns a structured response. The whole round trip usually takes milliseconds and happens thousands of times a day in a typical product.
- The client builds a request. A mobile app, browser, partner system or AI agent prepares a call, for example “give me the status of order 1042”.
- The request reaches the API. It often passes through an API gateway that handles TLS, routing and rate limits.
- The API authenticates and authorizes. It checks the token or key and confirms this caller is allowed to see this specific order.
- The API validates input. Malformed or unexpected data is rejected with a clear error instead of reaching the database.
- The business logic runs. The backend reads from a database, calls other services or triggers an action such as a payment.
- The API returns a response. Data comes back in an agreed format, usually JSON, with a status code.
- Everything is logged and measured. Latency, errors and usage feed monitoring and, for paid APIs, billing.
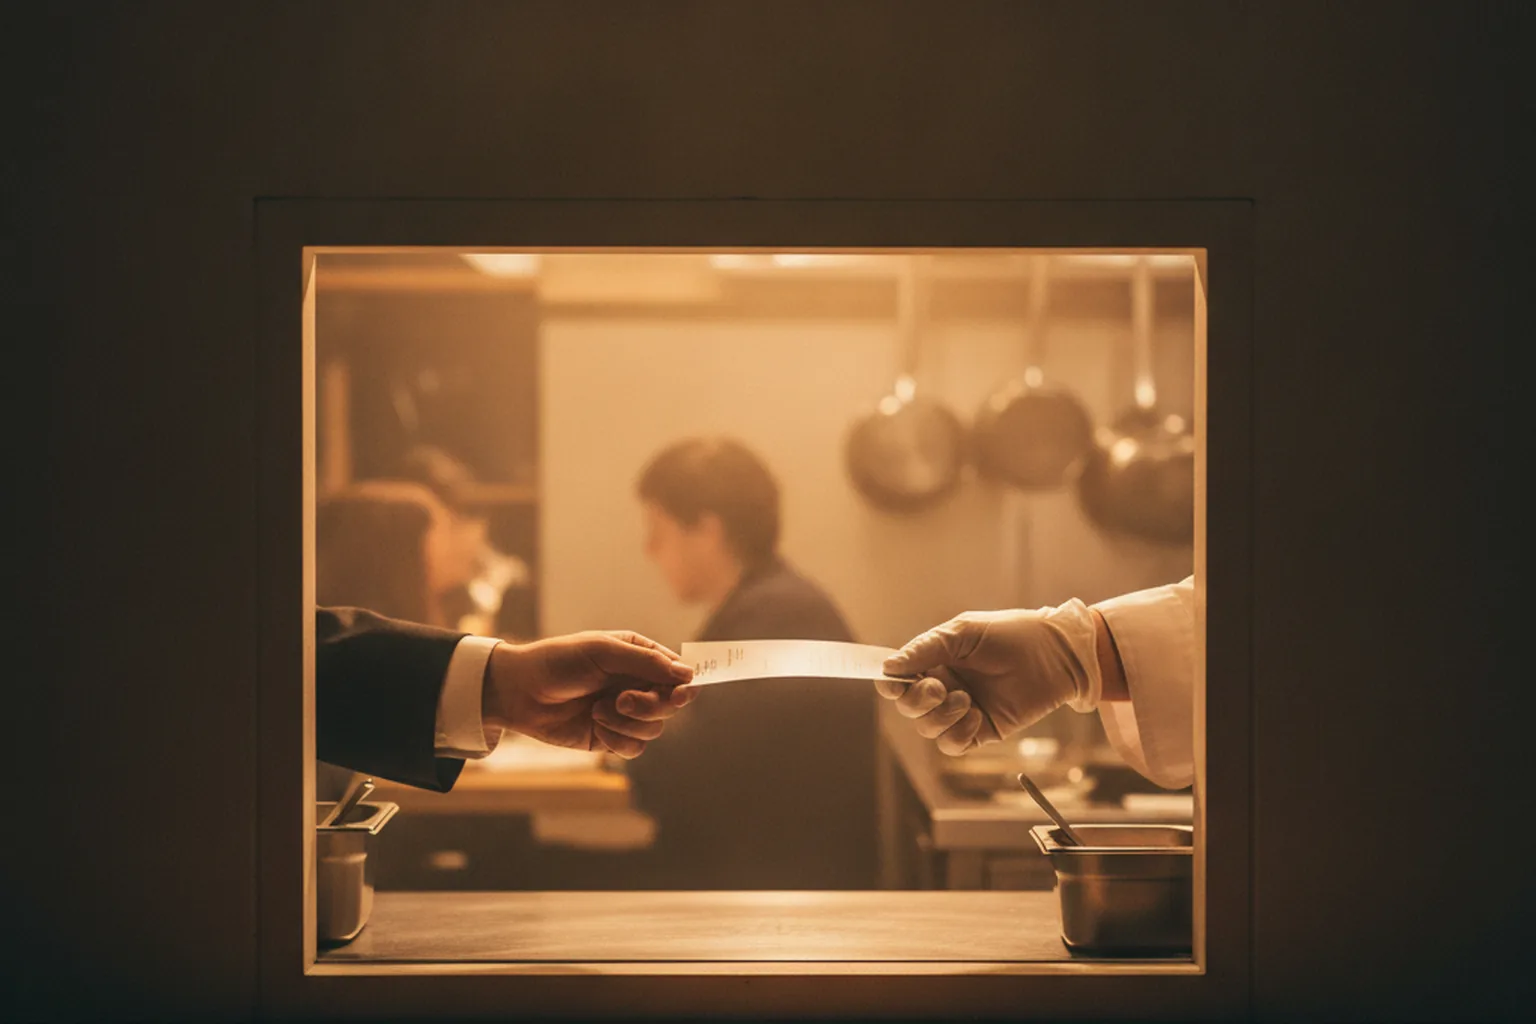
The classic analogy is a restaurant. You do not walk into the kitchen; you give your order to a waiter, who passes it through a window to the chef and brings back the dish. The menu is the API documentation, the waiter is the API and the kitchen is the backend system you never see.
Why do businesses need APIs?
Businesses need APIs because they let one backend serve many channels, partners and products without duplicating logic, while keeping data access controlled. A well-built API turns a company’s capabilities, such as pricing, inventory, payments or scheduling, into reusable building blocks.
- One backend, many clients. Web, iOS, Android, kiosks and internal tools all call the same API, so a business rule changes in one place.
- Security. Clients never touch the database directly; the API exposes only what each caller is allowed to see.
- Speed of delivery. Front-end and back-end teams can work in parallel against an agreed contract.
- Scalability. Services behind the API can be scaled, replaced or moved to another cloud without breaking clients.
- Partner ecosystems. Partners, resellers and marketplaces integrate through a documented API instead of custom one-off projects.
- New revenue. Data or functionality can be sold as an API product with usage-based pricing.
- AI readiness. AI agents and assistants act on your systems through APIs, so clean interfaces are a prerequisite for automation.
The numbers confirm the shift. Postman’s 2025 State of the API report, based on more than 5,700 developers and API professionals, found that 82% of organizations have adopted some level of an API-first approach and 25% operate as fully API-first. 69% of developers spend more than 10 hours a week on API-related work, and 43% of fully API-first organizations generate more than a quarter of their revenue from APIs.
What are the types of APIs?
APIs are usually grouped in two ways: by who can access them (public, partner, internal and composite) and by architectural style or protocol (REST, GraphQL, gRPC, SOAP, WebSocket and webhooks). The first grouping is a business decision; the second is a technical one.
Types of APIs by access
| Type | Who uses it | Typical example | Key requirement |
|---|---|---|---|
| Public (open) API | Any registered external developer | Maps, weather, payment provider APIs | Excellent docs, self-service keys, strict rate limits |
| Partner API | Selected partners under contract | Logistics carrier booking, insurer quoting, reseller ordering | Onboarding process, SLAs, partner-level access control |
| Internal (private) API | Teams and services inside one company | Backend for your own web and mobile apps, microservices | Consistency, speed of change, observability |
| Composite API | Clients that need several operations in one call | Create customer, order and invoice in a single request | Transaction handling and clear partial-failure rules |
Most companies start with internal APIs for their own apps and later open a subset to partners. Designing the internal API as if outsiders might use it one day, with clean naming and proper authorization, makes that step cheap instead of a rewrite.
REST vs GraphQL vs gRPC: which API style should you choose?
REST is the safe default for public and partner APIs, GraphQL suits products where many web and mobile screens need different shapes of the same data, and gRPC is the standard for fast service-to-service calls inside a backend. Most production systems in 2026 combine at least two of them.
| Style | How it works | Best for | Watch out for |
|---|---|---|---|
| REST | Resources at URLs, HTTP methods, usually JSON | Public and partner APIs, CRUD backends, caching | Over-fetching and many round trips on complex screens |
| GraphQL | One endpoint, clients query exactly the fields they need | Rich web and mobile apps, aggregating many services | Query cost control, caching and authorization per field |
| gRPC | Binary Protocol Buffers over HTTP/2, generated clients | Internal microservices, low latency, streaming | Limited native browser support, harder to debug by hand |
| SOAP | XML envelopes with strict WSDL contracts | Legacy banking, insurance and government systems | Verbose payloads, heavier tooling |
| WebSocket | Persistent two-way connection | Chat, live dashboards, trading, collaboration | Connection scaling and reconnection logic |
| Webhooks | The server calls the client’s URL when an event happens | Payment confirmations, status updates, integrations | Retries, signature verification, idempotency |
A common 2026 pattern is REST with OAuth 2.0 at the edge for partners, GraphQL or a backend-for-frontend layer for the company’s own apps, and gRPC between internal services. For a deeper comparison of the two most popular options, read our guide to REST API vs GraphQL.
What are everyday examples of APIs?
Everyday API examples are everywhere: any time two services exchange data without a person copying it, an API is usually involved. These are the patterns businesses build or integrate most often.
- Payments. A checkout sends card details to a payment provider’s API and receives an approval, then gets a webhook when the money settles. See our payment gateway integration guide.
- Banking. Budgeting and lending apps read account data through open banking APIs under PSD2 in Europe and similar frameworks elsewhere.
- Login. “Sign in with Google or Apple” uses OAuth 2.0 and OpenID Connect APIs.
- Maps and travel. Booking sites query many airline and hotel APIs at once and merge the results.
- Shipping. E-commerce stores request rates, print labels and track parcels through carrier APIs.
- Business systems. ERP, CRM, HR and accounting tools sync records through APIs instead of nightly CSV exports.
How does the API development process work?
A professional API development process runs in eight steps, from discovery to versioned operation, with the contract designed and agreed before most of the code is written. This design-first approach catches misunderstandings when they are cheap to fix.
- Discovery. Define who will call the API, which business capabilities it exposes, expected traffic, latency targets and compliance rules such as GDPR, HIPAA or PCI DSS.
- Contract design. Write the API specification first, usually in OpenAPI for REST, a GraphQL schema or Protobuf files for gRPC. Agree naming, pagination, error format and versioning rules.
- Review and mock. Share the contract with front-end, mobile and partner teams and generate a mock server, so clients can start building before the backend exists.
- Implementation. Build the endpoints, business logic, data access and integrations, keeping the code aligned with the contract through generated types or contract tests.
- Testing. Run unit, integration, contract and load tests, plus negative tests for invalid input and unauthorized access.
- Security hardening. Add authentication, object-level authorization, rate limits, input validation, secrets management and security scanning.
- Documentation and developer portal. Publish reference docs from the specification, add guides, code samples, a sandbox and a changelog.
- Deployment, monitoring and versioning. Deploy behind a gateway, monitor latency, errors and usage, and evolve the API with a clear deprecation policy.
The process is the same whether the API powers a single web app or a partner ecosystem; what changes is the depth of steps 6 to 8. A public API needs a far more polished portal and stricter limits than an internal one.
Which tools and technologies are used for API development in 2026?
API development in 2026 relies on a standard toolchain: a specification format, a backend framework, a gateway, testing tools and observability. The exact choice matters less than using the same tools consistently across all your APIs.
| Layer | Purpose | Common choices in 2026 |
|---|---|---|
| Specification | Machine-readable contract | OpenAPI 3.1 and 3.2, GraphQL SDL, Protocol Buffers, AsyncAPI for events |
| Backend frameworks | Implement endpoints and logic | Node.js (NestJS, Fastify), Python (FastAPI, Django REST), Java (Spring Boot), .NET, Go |
| API gateway | Routing, auth, rate limits, analytics | Kong, AWS API Gateway, Azure API Management, Apigee, Envoy-based gateways |
| Testing | Functional, contract and load tests | Postman, Pact, k6, Schemathesis |
| Documentation | Reference docs and portals | Redoc, Swagger UI, Stoplight, custom developer portals |
| Identity | Authentication and authorization | OAuth 2.0 / OpenID Connect providers, mTLS for service-to-service |
| Observability | Logs, metrics, traces | OpenTelemetry, Prometheus, Grafana, cloud-native monitoring |
Framework choice usually follows the rest of your stack. Our comparison of Node.js vs Python for the backend covers the trade-offs for the two most common API languages, and the broader picture of server-side work is in what back-end software development is.
How do you secure an API?
You secure an API by authenticating every caller, checking authorization on every object, validating all input, limiting usage and keeping an up-to-date inventory of every endpoint you expose. Most real-world API breaches come from missing authorization checks, not from broken encryption.
The OWASP API Security Top 10 (2023 edition) is the reference list of what goes wrong:
- Broken object level authorization (BOLA): a user changes an ID in the URL and reads someone else’s data.
- Broken authentication: weak tokens, missing expiry or brute-forceable login endpoints.
- Broken object property level authorization: the API returns or accepts fields the caller should not see or change.
- Unrestricted resource consumption: no limits on request size, rate or cost, inviting abuse and bill spikes.
- Broken function level authorization: ordinary users can call admin operations.
- Unrestricted access to sensitive business flows: bots automate purchases, sign-ups or bookings at scale.
- Server-side request forgery (SSRF): the API fetches a URL supplied by an attacker.
- Security misconfiguration: verbose errors, open CORS, missing TLS settings.
- Improper inventory management: forgotten old versions and test endpoints left online.
- Unsafe consumption of APIs: trusting data from third-party APIs without validation.
In practice that means OAuth 2.0 with short-lived tokens, authorization checks in the business layer rather than only at the gateway, schema-based input validation, rate limits per client, secrets in a vault and automated security tests in CI. Our checklist of web app security best practices covers the surrounding application layer.
How much does API development cost in 2026?
API development in 2026 typically costs $5,000–$15,000 for a single integration, $25,000–$60,000 for a small internal API and $60,000–$150,000 for a production public or partner API. Enterprise API platforms start around $150,000. The main cost drivers are the number of endpoints, integration complexity, security and compliance requirements, and the level of documentation partners need.
| Scope | What is included | Typical timeline | Estimated cost (US/EU vendors) |
|---|---|---|---|
| Third-party API integration | Connect one external API (payments, CRM, shipping), error handling, tests | 1–4 weeks | $5,000–$15,000 |
| Internal REST API | 10–20 endpoints for your own web or mobile app, auth, tests, docs | 4–8 weeks | $25,000–$60,000 |
| Public or partner API | Versioned contract, OAuth 2.0, rate limits, developer portal, sandbox, SLAs | 2–4 months | $60,000–$150,000 |
| Enterprise API platform | Gateway, many domains, event streaming, compliance, partner onboarding | 4–9 months | $150,000–$400,000+ |
Running costs are often forgotten: plan roughly 15–20% of the build cost per year for maintenance, security updates and new versions, plus gateway and hosting fees. Rates differ widely by region; our 2026 software development cost benchmark breaks down hourly rates by location.
What are the main challenges of producing and consuming APIs?
The main API challenges are not technical novelty but discipline: keeping contracts stable, documentation current and access under control as the number of clients grows. Teams that build APIs and teams that consume them face different problems.
Challenges when producing APIs
- Breaking changes. Renaming a field can break every client; versioning and deprecation policies prevent this.
- Documentation drift. Hand-written docs fall behind the code; generating docs from the specification solves it.
- Inconsistent design. Different teams invent different naming, errors and pagination; an API style guide and linting keep them aligned.
- Performance under load. N+1 queries and chatty endpoints appear only with real traffic; load testing finds them first.
Challenges when consuming APIs
- Unreliable third parties. External APIs time out or change; retries with backoff, circuit breakers and fallbacks are essential.
- Rate limits and quotas. Unexpected limits can stop a business process; caching and queueing smooth the load.
- Data quality. Responses from partners must be validated before they reach your database.
- Integration sprawl. Dozens of point-to-point integrations become hard to maintain; see our enterprise system integration guide for hub and event-driven alternatives.
How are AI agents changing API development?
AI agents are becoming a new class of API client, so in 2026 APIs need to be understandable and safe for software that reasons about them, not only for human developers. Clear descriptions, predictable errors and fine-grained permissions now matter as much as raw performance.
Postman’s 2025 report found that 89% of developers use AI tools, but only 24% design APIs with AI agents in mind. The Model Context Protocol (MCP), introduced by Anthropic in November 2024 and since adopted widely across the industry, gives agents a standard way to discover and call tools, and many of those tools are thin wrappers around existing APIs. Practical steps to make an API agent-ready:
- Write precise, human-readable descriptions for every operation and field in the specification.
- Return structured, actionable error messages an agent can recover from.
- Scope tokens narrowly, so an agent can read data or draft an action without full write access.
- Require human confirmation for irreversible operations such as payments and deletions.
- Log agent calls separately to audit what automated clients did and why.
If you are connecting language models to your systems, our generative AI integration services team usually starts by reviewing the existing API layer, because agent projects succeed or fail on the quality of the interfaces underneath.
Who builds APIs, and should you hire an API development partner?
APIs are built by backend or API developers, supported by solution architects, QA engineers and DevOps specialists. You can build in-house, hire a partner or combine both; the right choice depends on how central the API is to your product and how quickly you need it.
An API developer’s core responsibilities include designing contracts, implementing endpoints and integrations, writing automated tests, securing access, documenting the API and monitoring it in production. On larger projects an architect owns the overall API strategy and style guide.
When evaluating an API development partner, check that they:
- Design contracts first and can show OpenAPI or GraphQL specifications from past projects.
- Treat authorization, rate limiting and the OWASP API Top 10 as part of the default scope.
- Deliver automated contract and load tests, not only manual QA.
- Generate documentation from the specification and offer a sandbox for partners.
- Have a clear versioning and deprecation policy.
- Hand over code, infrastructure as code, runbooks and dashboards so you can own the API.
Our general guide on how to choose a software development company covers contracts, engagement models and red flags in more depth.
Key takeaways
- API software development is the design, build, testing, security, documentation and operation of the contracts that let software talk to software.
- In software development, API means application programming interface: a stable set of requests and responses that hides internal code.
- Design the contract first (OpenAPI, GraphQL schema or Protobuf) and let clients build against mocks in parallel.
- REST is the default at the edge, GraphQL for data-rich apps and gRPC for internal services.
- Most API breaches come from missing object-level authorization; follow the OWASP API Security Top 10.
- Typical 2026 estimates: $25k–$60k for an internal API, $60k–$150k for a public or partner API, $150k+ for an enterprise platform.
- AI agents are a new class of API client: precise descriptions, structured errors and narrow permissions make APIs agent-ready.
FAQ
What is API software development?
API software development is the work of designing, building, testing, securing, documenting and operating application programming interfaces: the contracts that let one piece of software request data or actions from another. It covers interface design (usually with an OpenAPI or GraphQL schema), the backend logic behind each endpoint, authentication, rate limiting, versioning, documentation and monitoring.
What does API mean in software development?
In software development, API stands for application programming interface. It is a defined set of rules, endpoints and data formats through which one program can ask another program for data or to perform an action, without knowing how the other program works internally. A weather app calling a forecast service or a checkout calling a payment provider are both using APIs.
What are the 4 types of APIs?
By who can access them, the four common types of APIs are public (open) APIs available to any registered developer, partner APIs shared with selected business partners under contract, internal (private) APIs used only inside one organization, and composite APIs that combine several calls into a single request. Separately, APIs are grouped by style or protocol, such as REST, GraphQL, gRPC, SOAP and WebSocket.
How much does API development cost in 2026?
Typical 2026 market estimates for US and EU vendors are $5,000–$15,000 for a single third-party API integration, $25,000–$60,000 for a small internal REST API with 10–20 endpoints, $60,000–$150,000 for a production public or partner API with authentication, a developer portal and SLAs, and $150,000–$400,000 or more for an enterprise API platform with a gateway, many domains and compliance requirements.
How long does it take to build an API?
A simple internal API with a handful of endpoints can be designed and built in 2–4 weeks. A production-grade REST or GraphQL API with authentication, tests, documentation and monitoring usually takes 2–4 months. An enterprise API platform with a gateway, versioning policy and partner onboarding is typically delivered in phases over 4–9 months.
Should I use REST, GraphQL or gRPC for my API?
Use REST as the default for public and partner APIs because it is simple, cacheable and understood by every client. Choose GraphQL when web and mobile clients need many different shapes of the same data. Use gRPC for fast, strongly typed service-to-service communication inside your own backend. Many production systems combine REST at the edge with gRPC internally.
Published 30 October 2026. Sources: Postman, 2025 State of the API Report; OWASP API Security Top 10 (2023); OpenAPI Initiative specifications; Model Context Protocol documentation. Cost ranges and timelines are typical 2026 market estimates for US and EU vendors, not YuSMP Group quotes.